Skip to content

//DEFENCE SUPPLY CHAIN SECURITY ASSURANCE

EXPERTISE ON DEMAND

We evaluate suppliers against SC-CIS requirements, DCC compliance standards, and MOD security protocols. Our assessments include security policy reviews, technical control verification, incident response capability evaluation, and ongoing monitoring to detect emerging risks.

We provide detailed reporting that enables informed risk-based decisions about supplier relationships.

THIRD-PARTY RISK MANAGEMENT

Beyond initial assessments, we offer continuous monitoring and periodic re-evaluation of your supply chain partners. Our service includes risk scoring, remediation tracking, and escalation protocols for critical findings.

We work collaboratively with your suppliers to help them achieve required security standards while maintaining your operational requirements.

OUTSOURCED ASSURANCE MANAGEMENT

We can manage your entire third-party assurance programme, conducting independent reviews and audits on your behalf. This approach reduces internal resource requirements while ensuring consistent, professional evaluation of supply chain security.

Our flexible services scale with your budget and can be tailored to your specific risk appetite and compliance requirements.

WHY DEFENCE SUPPLY CHAIN SECURITY MATTERS

A single compromised supplier can provide attackers with access to classified information, sensitive project details, or critical defence infrastructure. Our supplier assurance services protect your organisation from supply chain attacks, ensure regulatory compliance, and maintain the integrity of defence operations.

Frequently Asked Questions

FIND OUT MORE ABOUT WHAT WE DO
improved-efficiency-1
What is supplier assurance? minus-icon

Supplier assurance is the process of evaluating and monitoring the security and compliance of third-party suppliers to ensure they meet the necessary standards and requirements.

Why is supplier assurance important? plus-icon
How does supplier assurance work? plus-icon
What are the benefits of supplier assurance? plus-icon
How can Periculo help with supplier assurance? plus-icon

Latest Insights

Binance's $6.3 Billion Security Incident: What We Know, and What May Have Happened

Binance's $6.3 Billion Security Incident: Wha...

Binance, the world's largest cryptocurrency exchange, suffered a security incident on 29 October 2026 in which an estima...
PHP2Shell: NCSC Warns UK Organisations to Patch PHP Now

PHP2Shell: NCSC Warns UK Organisations to Pat...

On 21 October 2026 the NCSC told UK organisations to take immediate action on two critical PHP vulnerabilities, CVE-2026...
DSPT 9.5.11: Software Security Code of Practice Explained

DSPT 9.5.11: Software Security Code of Practi...

Short answer: DSPT evidence item 9.5.11 is a new mandatory requirement for Category 2 IT suppliers in 2026-27. It requir...
Cyber Essentials Plus and ISO 27001 Help DSPT Submission

Cyber Essentials Plus and ISO 27001 Help DSPT...

Which of the 102 Category 2 Evidence Items You Can Skip Short answer: Category 2 IT suppliers must evidence 102 mandator...
Google Cloud Outage: What It Means for Your Business Continuity Plan

Google Cloud Outage: What It Means for Your B...

On 20 October 2026, a fault in Google Cloud’s europe-west2 (London) region knocked out multiple services and disrupted o...
DSPT 4.5.6 Explained

DSPT 4.5.6 Explained

The New MFA and Identity Federation Requirement for IT Suppliers Short answer: Evidence item 4.5.6 is a new mandatory re...
What Is a Data Subject Access Request (DSAR)? A Practical Guide

What Is a Data Subject Access Request (DSAR)?...

Short answer: A Data Subject Access Request (DSAR) is a request, made under Article 15 of the UK GDPR, for a copy of the...
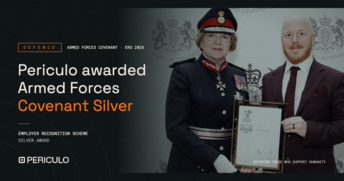
Periculo awarded Armed Forces Covenant Silver

Periculo awarded Armed Forces Covenant Silver

I'm proud to announce that Periculo has been awarded Silver in the Armed Forces Covenant Employer Recognition Scheme. Th...