Q3 has just closed, and there's no gentler way to say it: December is closer than it looks!!!
If your organisation supplies the Ministry of Defence, the clock is now running on the 31 December deadline for Defence Cyber Certification (DCC) Level 0.
At the same time, the NHS Data Security and Protection Toolkit (DSPT) for 2026–27 has opened its doors, though the audit requirements for IT suppliers are still to be confirmed. Don't worry we're watching closely and getting ready for updates.
On top of that, our AI-driven penetration testing agent has been busy this month, running continuous testing for a digital health client and turning up some impressive results along the way.
Read on to find out what has been going on at Periculo from another new team member, an update from the field, and this month's security tip...
Welcome to Periculo, Sam!
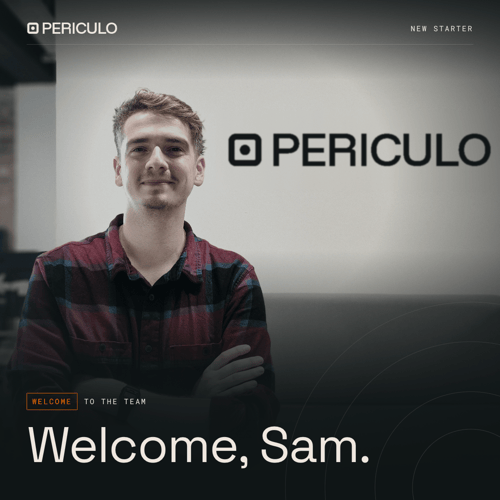
Periculo is delighted to welcome Sam Martin to the team this month.
After twelve years in generalist IT roles spanning helpdesk, sysadmin and operations, Sam moved into cyber security at the start of the year, discovering along the way that his real interest lies in the technical side of the field.
He joins the ever-growing Periculo, supporting the penetration testing and Cyber Essentials Plus teams.
NHS DSPT 2026-27 Is Open... But We Await the IT Supplier Audit Requirements
The NHS DSPT for 2026-27 went live on 4 September 2026. Version 9 is now aligned to the Cyber Assessment Framework (CAF) version 4.0, and organisations have until 30 June 2027 to complete their assessment.
For IT suppliers: most of what applies to you this year has already been published, but NHS England has not yet confirmed which specific areas it will select for mandatory audit. We'll get an update out as soon as the NHS confirms this.
In the meantime, we're getting ready on our end to start accepting provisional audit dates, so keep an eye out for that.
DCC Level 0: The MoD's 31st December Deadline
Defence Cyber Certification has quickly become one of the busiest parts of the business this quarter. We are now speaking with some exciting companies in the defence space directly, as well as a growing number of digital health companies whose work is starting to overlap into defence.
The Ministry of Defence's 31 December deadline for Level 0 is clearly getting partners to act now.
For anyone still weighing up their approach: Level 0 is typically the fast assessment to complete.
Periculo will credit the cost of a client's Level 0 assessment toward a higher Defence Cyber Certification level if they decide to pursue Level 1, 2 or 3 later.
In the Field
Our AI-driven penetration testing agent has been hard at work this month for digital health clients, running continuous, round-the-clock testing alongside our usual manual engagements.
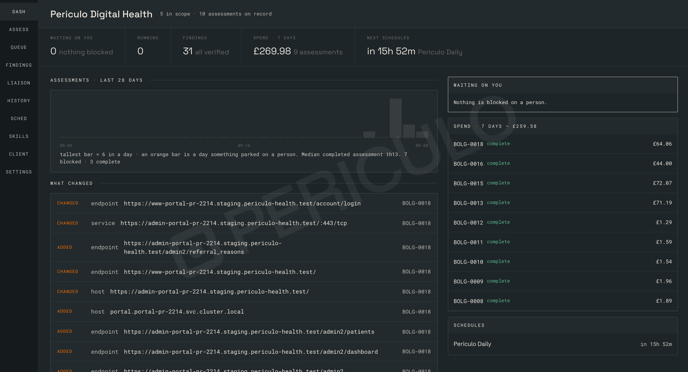
Where a traditional penetration test gives you a snapshot once or twice a year, this agent never really switches off, probing for weaknesses continuously rather than waiting for the next scheduled test. This month alone it completed several runs and surfaced multiple findings, including five rated high severity, all flagged automatically, all mapped and ready for the team to act on. That's a level of ongoing coverage that would be hard to match with manual testing alone.
It's not about replacing the judgement of our testers; it's about giving them a force multiplier, catching issues between engagements rather than letting them sit until the next scheduled test. If continuous, always-on penetration testing sounds like something your organisation should have, get in touch to find out more.
One Programme
If Periculo already looks after your Cyber Essentials, Cyber Essentials Plus, penetration testing, internal ISO 27001 audit or NHS DSPT, it's worth asking about our Assurance Programme rather than treating each of these as a separate annual task.
Instead of juggling different renewal dates, evidence requests and audit windows throughout the year, the Assurance Programme brings your certifications together under one ongoing, tiered monthly arrangement, with Periculo managing the framework, the evidence and the audit cycle on your behalf.
For organisations already stretched thin on compliance admin, the appeal isn't really about cost; it's about never being caught out by a renewal date nobody flagged in time.
If that sounds useful, get in touch
Security Tip of the Month
AI tools have become a normal part of how teams work, but it's worth pausing on what you're actually sending them.
Every prompt typed into a public AI tool is, in effect, data leaving your organisation and landing on someone else's servers, often to be retained or used for further training, depending on the terms you've agreed to without reading. Client names, contract details, source code and personal data have all ended up in free-tier AI tools this way, not through malice, but because someone was trying to save ten minutes.
The practical fix is less about banning AI outright and more about treating it like any other third-party supplier: know which tools your team is actually using (not just the ones you've sanctioned), check whether the provider trains on your inputs by default, and set a simple house rule that client-identifiable and commercially sensitive information doesn't go into a prompt unless the tool sits under a proper data processing agreement. Enterprise and business tiers of most major AI tools now offer this; free consumer versions generally don't.
If you'd like a second opinion on how your organisation's AI use looks from a security standpoint, get in touch.
Jargon Buster
CAF (Cyber Assessment Framework) is the framework published by the National Cyber Security Centre that underpins how organisations assess and improve their cyber resilience against a set of outcome-focused principles, rather than a simple checklist. The new NHS DSPT 2026-27 toolkit aligns with Version 4.0 of the CAF, which is why some of the DSPT's requirements this year will feel more outcome-based than in previous versions.
Get in Touch
Whether you're working against the DCC Level 0 deadline, waiting on NHS DSPT clarity, or want to make sure your certifications aren't creating more admin than they need to, our team is here to help. Get in touch, and we'll point you in the right direction.